What a Kill Switch Is and When to Turn It On

The moment a tunnel drops, something has to decide where your traffic goes next. That's the one question a kill switch answers, and skipping it is enough to leak something in just a few seconds.
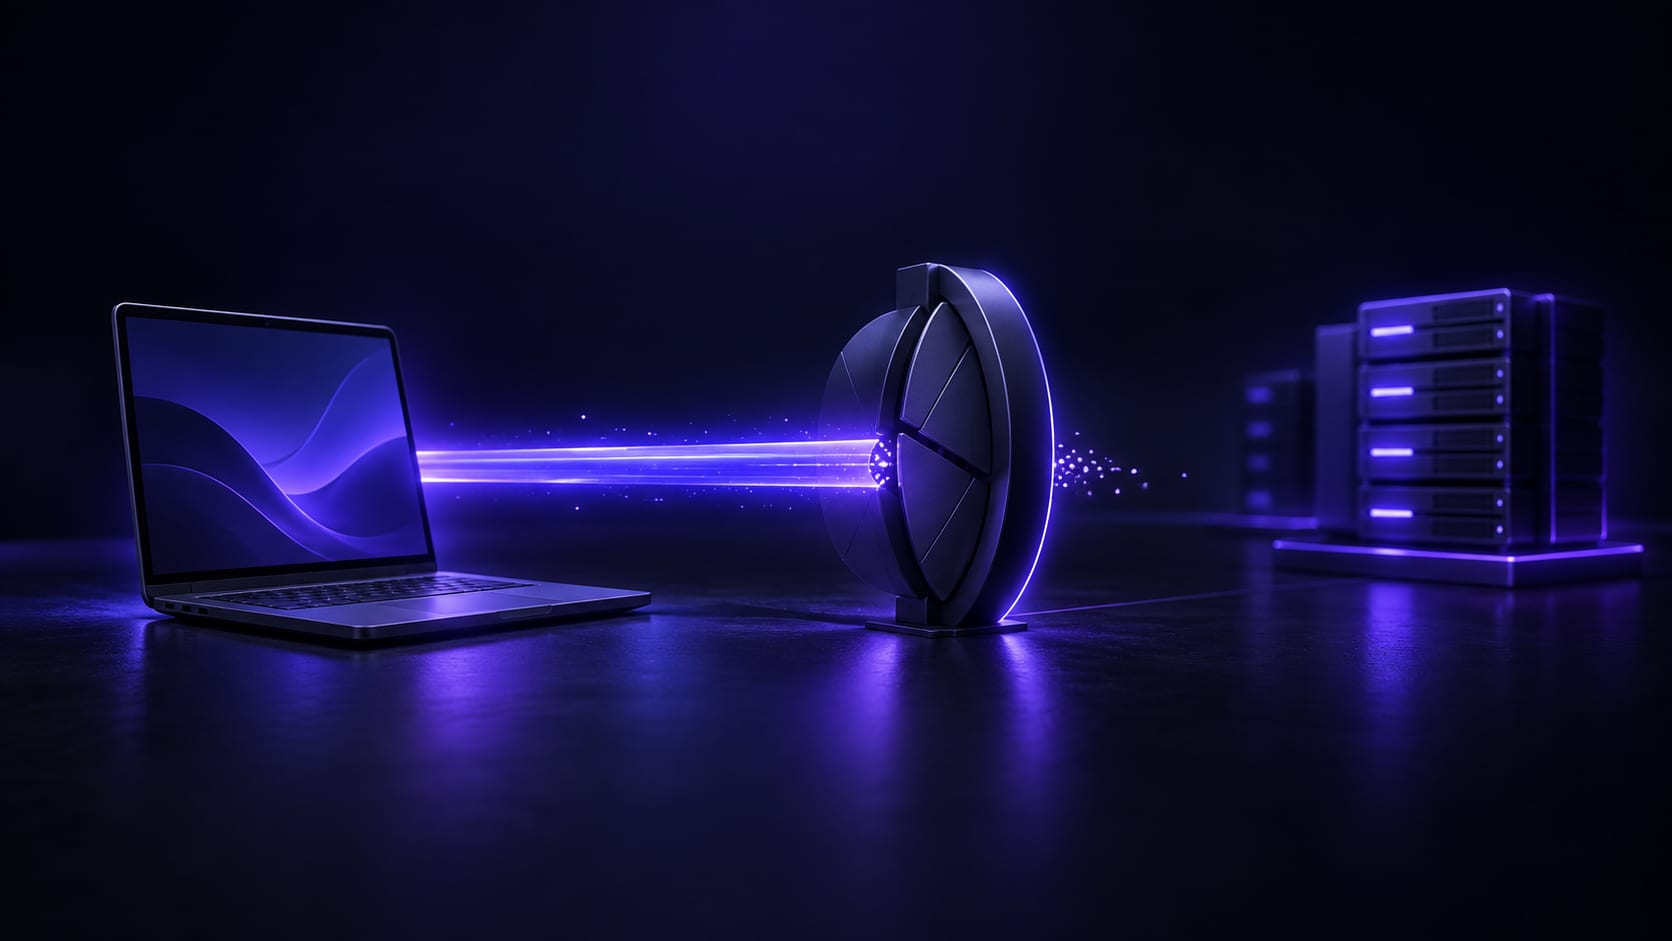


A kill switch does exactly one thing: the instant the tunnel drops unexpectedly, it cuts the whole device's network access so traffic can't quietly fall back to the unencrypted path.
It exists for one very specific gap. While the connection is healthy, this feature does nothing at all — you won't notice it's there. Only in the few seconds after a tunnel drops and before a new one is up does it step in and lock the network down temporarily. Skip that step, and those few seconds look like nothing more than a hiccup, while your traffic may already have quietly switched to the unencrypted default route.
Here's exactly when it fires, what it actually protects, why it can feel annoying, and what it has no say over.
What a kill switch actually does
A VPN tunnel isn't permanently stable — a dropped connection, switching nodes, or a device waking from sleep can all take it down in an instant. Normally the device falls back to a plain, unencrypted connection right away, and that handoff is usually so fast and quiet that most people never notice the gap in between.
A kill switch sits right in that gap. It keeps checking whether the tunnel is still alive, and the moment it isn't, it takes back network access immediately rather than letting the system decide on its own, holding it until the new tunnel is ready. During that stretch the device looks like it has no internet, but the trade is that those seconds never become the exception where something leaks.
The word "kill" sounds harsh, but all it cuts is the network — not the device itself, and not a form you're filling in or a file saved locally. Once the connection is back, most things just carry on; at worst, the page you were on needs a refresh.
When it actually fires
The most common triggers:
- Switching nodes by hand, in the second or two between the old tunnel closing and the new one coming up
- Wi-Fi and mobile data switching automatically as the network interface reinitializes
- A computer or phone waking from sleep before the network stack is fully back
- The current network itself being unstable, dropping the tunnel and forcing it to renegotiate
What these all have in common: the drop is brief and usually resolves itself within seconds, but the risk during that short window is nothing like the risk during a stable connection. Telling them apart isn't hard — if you just switched nodes yourself or just unlocked the screen, it's almost certainly one of the first two; if nothing changed and the network just vanished, the network itself is more likely unstable, and that kind of drop can keep recurring even after you change nodes.
What it actually protects against
It protects against exactly this leak during the gap. Without a kill switch, the moment a tunnel drops, the browser and every app keep sending whatever they were sending — just over the unencrypted default connection instead. Your real IP and the domains you're visiting can be exposed for those few seconds, often without you noticing at all, because the page may still load fine; it just took a different route to get there.
A kill switch turns that gap from "quietly leaks" into "goes offline first, comes back once it's safe." The cost is a brief inconvenience; what you get in return is that those seconds never become the exception.
Why it can be genuinely annoying
A kill switch doesn't distinguish a sensitive connection from an ordinary one — it acts globally. So an entirely routine network switch, like walking from your home Wi-Fi into an elevator and onto mobile data, takes a half-downloaded file, a video mid-playback, and a background email sync down with it for a moment.
For anyone in a hurry, those few seconds of "suddenly offline" are easy to mistake for a fault, and the effect is far more noticeable for anyone constantly switching between Wi-Fi and mobile data. The extreme case is riding the subway — signal flickers in and out, the system keeps hopping between Wi-Fi, data, and nothing, and the kill switch fires right along with it, which gets old fast. That's exactly why it's usually built as something you can switch on or off yourself, not something forced on permanently.
How to actually use it
Work out whether it's "cut everything" or "just block new connections"Implementations differ in how strict they are: some cut everything, including connections already established; others only block new ones, leaving whatever's already transferring untouched. Both get called a kill switch, but they're not remotely the same in practice — know which one you're dealing with before deciding whether to turn it on.
Turn it on only when you need the strict versionFor everyday scrolling and video, a few seconds offline that resolve on their own is fine — you don't need a kill switch running for that. Before a bank transfer or logging into an important account, turning it on first is the safer call; a few extra seconds of waiting beats even one instance of a leak.
Pair it with auto-reconnectA kill switch stops leaks the moment the tunnel drops; auto-reconnect gets the tunnel back up as fast as possible. Run both and the experience is "briefly offline, back quickly." Run the kill switch alone without auto-reconnect, and it can turn into "offline until you tap reconnect yourself."
Treat phones and computers as separate casesA mobile device switches between Wi-Fi and data far more often than a computer does, so a kill switch fires more often there too. If it feels too frequent on your phone, check first whether the cause is the network switching itself before rushing to turn the feature off; a computer usually stays on one network, so it fires rarely enough that you'll barely notice it's on.
What a kill switch does not protect against
It protects traffic after the tunnel drops — it has no say in why the tunnel dropped in the first place. If the cause is an unstable node, a kill switch will just make you notice "no internet" more often without making that node any more stable; the actual fix is still switching nodes, and diagnosing a dead connection covers that approach.
It also has nothing to do with traffic that already went out before the drop — that data was already on its way while the tunnel was still alive, and how safe it was depends entirely on that connection at the time. If what worries you is DNS resolution leaking on its own, that's a separate problem; checking for a DNS leak covers that exact layer, which a kill switch doesn't touch.
It's also worth knowing a kill switch governs the system-level network exit — if some app bypasses the system proxy and connects directly on its own, a kill switch can't stop that app's traffic either. That's uncommon, but it happens, and it's not a reason to treat a kill switch as some final, universal safety net.
Don't confuse it with "the public network itself is now safe," either. On public Wi-Fi, most of the risk comes from fake hotspots and phishing login portals, and a kill switch does essentially nothing about either — it only cares whether the tunnel itself is up, not whether the network you joined has a problem of its own. Keep the two separate, or it's easy to assume turning on a kill switch makes a shady public network safe, which it doesn't.
In summary
A kill switch solves one narrow but genuinely useful problem: whether traffic should be allowed through during the few seconds a tunnel drops unexpectedly. The answer is no, so it goes offline first to make sure those seconds never become the exception. It doesn't fix why the drop happened, doesn't cover data sent before it, doesn't reach an app that bypasses the system proxy, and doesn't make an unsafe public network safe — strictly speaking, it only ever covers this one gap.
Whether the occasional inconvenience is worth it depends on what you're doing. For scrolling and video, a few offline seconds that resolve themselves are fine; before a transfer or an important login on a public network, turning it on first is the safer trade — a few extra seconds for that certainty is worth it. FastOrange pairs its kill switch with auto-reconnect, so it comes back fast and never leaves a gap open in the meantime; the encryption behind it is on the security page. Every account gets free daily trial time after signup if you want to see how fast the reconnect really is — see the details.
 High speed
 Millions of users
 24/7 Support
Get the Fast Orange App
One App. Every Platform. A More Stable Connection.
Available for Windows, macOS, Android, and iOS. Use One Account Across All Your Devices and Start with a Free Trial.
High speedMillions of users24/7 SupportDownload Fast Orange
 Choose your platform
Download Fast Orange
Switch between Windows, Android, iOS, and macOS