VPN Encryption Basics: What It Actually Protects

"Encryption" gets treated as an all-purpose safety label, but it actually does one specific job: making the content unreadable to anyone watching along the way. Here's exactly which stretch of the trip it covers, and which problems it simply doesn't touch.


"Encryption" gets treated like an all-purpose safety label, as if using it makes everything safe. In reality it does one very specific job: turning the content of your data in transit into something unreadable to anyone watching along the way. It doesn't cover your account's security, and it doesn't cover your device's security — the two get lumped in together constantly, but they're completely separate lines of defense.
Here's exactly which stretch of the trip encryption covers, what it blocks, and which problems it simply doesn't reach — meant to take the word "encryption" apart into something specific, rather than treat it as one vague, reassuring word. There won't be a specific algorithm name or key length in here: comparing those numbers in public doesn't tell you much that matters. What's actually worth understanding is the scope of what encryption covers in the first place.
Before deciding whether encryption matters for a given situation, ask one question first: is the worry "my content being seen," or "my identity or account being recorded" — the answers to those two are often different, and answering both with the same word is exactly why "encryption" ends up sounding vague.
Which stretch of the trip encryption actually covers
Split one connection into three stretches, and encryption only does real work on the middle one:
- Device to the app itself — this stretch is usually the responsibility of the device's own operating system, and has little to do with the encryption a VPN handles.
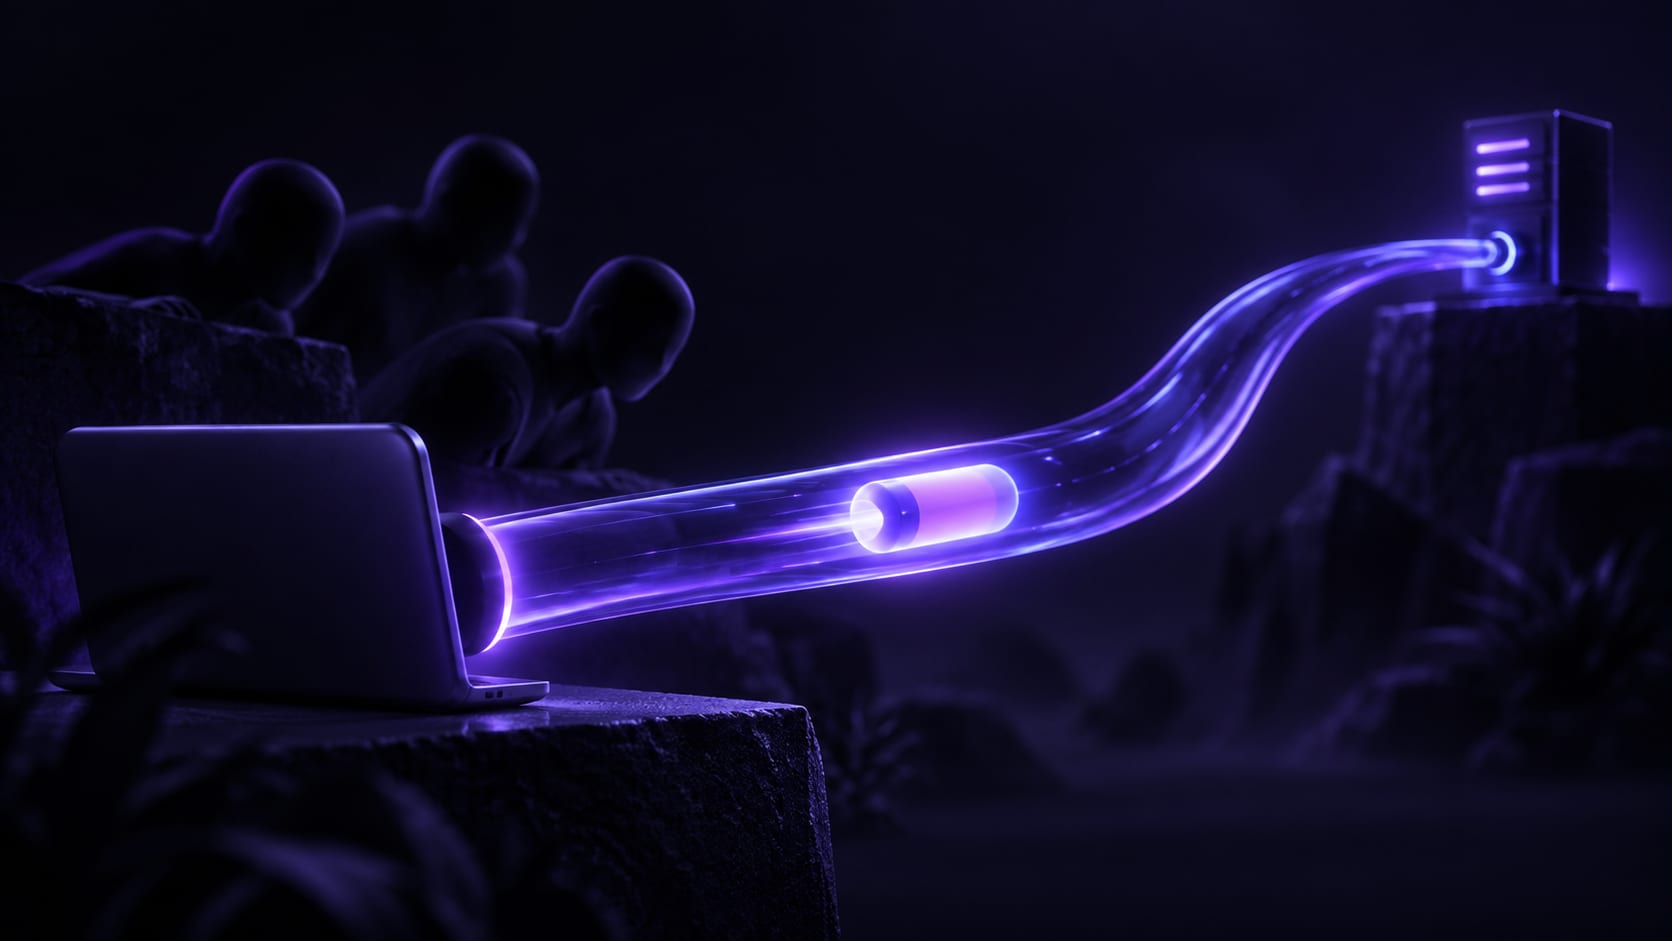
- App to the node — this is where VPN encryption actually does its job. Once data leaves the device it's wrapped in a layer of encryption; anything in between, including the Wi-Fi you're on and your carrier, can see that data is moving and roughly where, but can't read what's inside it.
- Node to the destination site — if the destination site itself uses an encrypted connection (the lock icon in the address bar), that stretch already has its own protection, stacked on top; if the destination site doesn't use encryption, a VPN has no way to add that layer on its behalf — that's the destination site's own responsibility, regardless of whether you're using a VPN.
HTTPS and a VPN solve different problems
The lock icon in the address bar, HTTPS, and a VPN's encryption get treated as two names for the same thing. They actually protect completely different, non-overlapping ground, and leaving either one out leaves a gap the other one doesn't cover.
HTTPS protects the stretch between the device and one specific site. As long as that site supports it, that content is unreadable along the way, VPN or no VPN. But it only covers that one site — other sites open at the same time that don't use HTTPS aren't protected the same way, and it never hides which site is being visited in the first place. The network in use can usually still see which domain is being opened, just not what's actually being sent to it.
VPN encryption covers a different stretch: device to node. Regardless of which site comes next, or whether that site itself uses HTTPS, this stretch is wrapped in its own layer first, so the local network only sees a block of encrypted traffic headed to the node, with no visibility into which domain is actually being reached. That fills in exactly what HTTPS doesn't cover: the question of which site is being visited at all.
That's the reason to run both rather than treat one as a substitute for the other: with only HTTPS, the local network can't read the content but can still see the domain; with only a VPN, if the destination site itself doesn't use HTTPS, the stretch from node to that site becomes the one part left uncovered — exactly the case described earlier as "node to destination site." Each one covers a different stretch, and only stacked together do they cover the whole trip.
What encryption actually blocks
It blocks "content," not the fact that something is being transmitted at all — anyone along the way can still see that encrypted traffic is passing through, they just can't read what's inside it. This matters most on public Wi-Fi: at an airport or coffee shop, on a password-free or shared-password hotspot, other devices on the same network could, in principle, see the content of unencrypted traffic. With this layer added, what they see instead is a block of unreadable data, no different from looking at gibberish.
Put another way, the value of this layer doesn't depend on "whether someone is actually watching" — it's about "what they'd see if they were." Most of the time nobody is actually watching a given public Wi-Fi network, but the point of this layer is exactly that you don't have to bet on those odds.
What encryption doesn't cover
- Account security — password strength and whether extra verification is on are a completely separate line of defense, unrelated to whether the transit link is encrypted.
- Whether the destination site recognizes "you" — whatever account you log into and whatever you type into a form is recorded by that site in full; encryption only protects the trip there, not what the site does once it arrives.
- Making the device itself more secure — malware, a lost device, someone else unlocking it — none of that has anything to do with encryption on the transit link.
- Hiding the fact that you're "using a VPN" at all — a network administrator can usually see that encrypted traffic is passing through and which node it's headed to, just not the content. That's not the same thing as being completely invisible.
- Fully erasing behavioral patterns in the traffic — the content itself becomes unreadable once encrypted, but the timing of connections and the size and rhythm of data packets can, in principle, still hint at "roughly what kind of thing is happening." That's a different layer of the problem from "can the content be read," and blurring the two leads to a false sense of security.
A common misunderstanding
A common line is "encryption means I'm completely safe," which treats "unreadable content" and "completely safe" as the same thing — they aren't. Take an example: encryption stops someone along the way from reading your content, but it does nothing to stop you from typing your own account password into a phishing site. In that scenario, the data is still encrypted in transit; the problem is trusting the wrong destination, not encryption failing at its own job.
The same logic applies to the device itself: a phone infected with malware, or with spyware quietly installed on it, is reading content the device could already see on its own — that has nothing to do with whether the transit link is encrypted. Encryption solves problems "on the way." It doesn't solve problems that already exist at either end.
How to think about this now
Deciding whether encryption matters for you starts with naming the actual scenario. Worried about "someone on public Wi-Fi seeing the content of my traffic" — encryption directly handles that. Worried about "my account getting stolen" or "what happens if I lose my device" — that comes down to password management and the device's own security settings, and encryption can't help there. FastOrange encrypts content in transit and pairs that with a no-logs policy, together handling whether content can be read and whether a record gets kept — but the account and the device are still down to your own habits. For exactly what a no-logs policy promises and what it doesn't reach, what a no-logs policy actually means breaks that down in more depth. To start from an even more basic question of what a VPN solves in the first place, what a VPN is covers that from the ground up.
In summary
Encryption protects the content of data on the stretch between your device and the node, keeping anyone watching along the way from reading what's inside — it doesn't cover account security, doesn't cover device security, and doesn't hide the fact that you're using a VPN in the first place. Keeping these apart is what tells you which of your actual worries encryption solves.
If what you're worried about is content being read on a public network, this layer already covers it. If what you're worried about is your account or your device, that takes separate attention — encryption doesn't reach either end, and treating it as one blanket layer of protection is exactly what leads people astray. FastOrange handles encryption of content in transit along with a no-logs policy, and every registered account gets free trial time daily — try it first, then decide whether it's worth keeping long term.
 High speed
 Millions of users
 24/7 Support
Get the Fast Orange App
One App. Every Platform. A More Stable Connection.
Available for Windows, macOS, Android, and iOS. Use One Account Across All Your Devices and Start with a Free Trial.
High speedMillions of users24/7 SupportDownload Fast Orange
 Choose your platform
Download Fast Orange
Switch between Windows, Android, iOS, and macOS