How a VPN Actually Works: The Path Your Data Takes

How a VPN works, in one line: the device connects to a middle node first, and the node forwards everything from there. This walks through what happens in order, including whether DNS follows the same tunnel and why the IP a site sees changes.
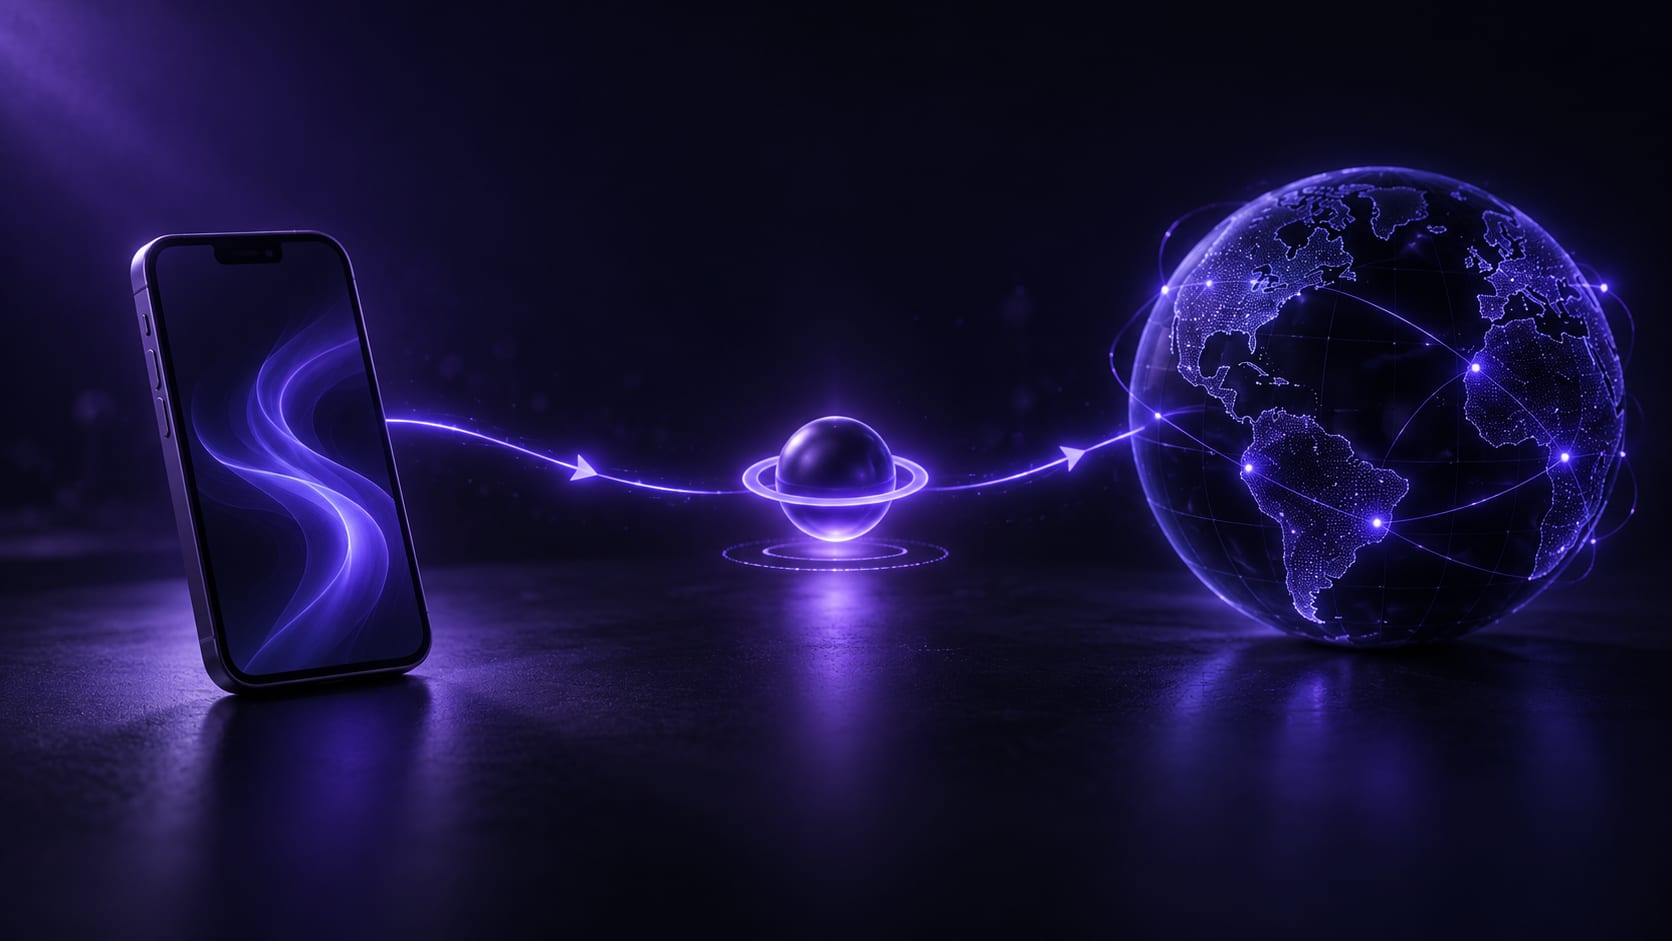


How a VPN works comes down to one line: the device stops talking to the destination site directly, and instead connects to a middle node first, which forwards everything on its behalf. This walks through what happens along that path in the order it actually happens, including DNS and the IP change — the two things people mix up most.
To get the bigger picture of what a VPN solves and where it shows up day to day, what a VPN is covers that from the ground up. This one assumes you already know why you'd connect one, and focuses entirely on where the data actually goes once it's up.
First, how data travels without a VPN
Without a VPN, a request leaves the device for the local network (a home router, or a phone tower), then passes through the carrier's network before reaching the destination site. Along that path, the carrier can see which site you're connecting to, and roughly when and for how long; if the destination site itself isn't using an encrypted connection, the carrier could in theory see the content too.
This path is the default, and most people never notice it exists — not until there's a reason to add another layer, at which point it's worth knowing what the default actually looked like. Seeing a connection at all isn't news to the carrier — routing only works because every hop along the way knows where to forward things next. What a VPN changes isn't whether that happens, but where it happens.
Once a VPN connects, the path gains one more leg
Step one: the device connects to the VPN node firstOpen the VPN and tap connect, and the first thing the device does is establish an encrypted connection to whichever node the provider assigned. Once that's up, every network request from that point on goes through it first, instead of heading straight for the destination site. This step usually takes a few seconds, and the status flipping from "not connected" to "connected" is the signal that it's done — nothing else needs doing by hand after that; the forwarding that follows happens automatically.
Step two: the node forwards the requestOnce the request reaches the node, the node strips the encrypted outer layer, reads the actual destination address inside, and forwards the request onward under its own identity — its own IP. What the destination site receives looks like it came from the node, not from the device itself. This is also exactly why a site's guess at "where you are" ends up following the node instead — more on that below.
Step three: the destination site sends content back to the nodeThe destination site processes the request and sends the content back to whoever asked for it — the node. Nothing about this step differs from ordinary browsing; the destination site has no way of knowing who's connected on the other side of the node. As far as it's concerned, this looks like an ordinary visit initiated by the node itself.
Step four: the node encrypts the content and sends it back to the deviceThe node takes what the destination site sent back, encrypts it again, and returns it along the same connection that was established at the start; the device decrypts it, and only then does the page or app actually show anything. The whole round trip usually takes a fraction of a second — nothing about the extra hop is noticeable day to day, browsing or streaming feels about the same as connecting directly, unless the route itself is having a bad day, in which case the extra leg becomes noticeable.
What DNS is actually doing in the middle of this
Opening a site starts with the device converting the domain name you typed or tapped into a numeric address — that step is called a DNS lookup, and day to day it's basically looking up a number in a phone book: you know the name, but dialing requires the number first. A browser or app does the same lookup before it knows where to even send the request, and this happens before any actual data transfer — an easy step to overlook in the whole chain.
If that DNS step doesn't travel through the VPN tunnel and instead keeps using the local network's own lookup path, a "split" shows up: the bulk of the traffic goes through the encrypted tunnel, but that one small DNS step still completes on the local network, which means the local network can still see which domains were being looked up — indirectly learning which sites were visited, even though the main traffic itself was encrypted. This has its own name, and what a DNS leak is and how to check for one covers exactly how to test for it and confirm whether it's happening. A properly built VPN client routes DNS lookups through the same tunnel as everything else, so the local network can't see even that much — nothing for the user to manage by hand.
Why the IP address you show up as changes
Sites and apps judging "where you are" rely heavily on the IP address the connection arrives from. Without a VPN, that's your own network's outbound address; once connected, the node forwards the request under its own identity, and the address the site sees becomes the node's instead of the device's own. It's also why the region a node sits in affects what a site shows — language, currency, sometimes even whether certain pages open at all can shift along with that address.
| What changes | Without a VPN | Once connected |
|---|---|---|
| Outbound IP the destination site sees | Your own network's address | The node's address |
| Whether the local network sees which site you visited | Yes | Usually not — just that a VPN is connected |
| The rough region a site infers | Wherever your own network is | Wherever the node is |
Everything in that table is a change at the address level, not a disappearance — the site still receives an address, it's simply the node's instead. The site's own logic for judging things keeps running exactly as before; only the signal feeding into it changed. Placed next to the "how data travels without a VPN" section above, the picture gets clearer: nothing new was invented here, one more stop — the node — was inserted partway through the same path that was already there.
Why switching nodes sometimes triggers a fresh verification
Plenty of sites and apps treat "the address a connection arrives from" as one signal for judging whether the same person is using the same session. Switch nodes, and that signal changes along with it — some services respond by asking for identity verification again, or requiring a fresh login. That's not a VPN malfunctioning; it's the other side's own logic treating an address change as something worth double-checking, which is a normal reaction on its part.
VPN login failures and missing verification codes covers exactly what to do when this comes up — switching back to the previous node, or simply staying on one node, usually cuts down on how often this happens. The logic is simple: fewer signals changing gives the other side fewer reasons to ask again. If the IP still shows up as a mainland address after connecting, instead of the node's, IP still shows China after connecting to a VPN covers exactly that case, and it runs on the same underlying logic as this page.
In summary
How a VPN works, stripped down: the device connects to a node, the node forwards on its behalf, the destination site sends content back to the node, and the node sends it back to the device — the whole round trip riding the same encrypted tunnel both ways. Two details in that path are the easiest to overlook and the most worth understanding: whether DNS lookups travel through the same tunnel, and whether the IP a site sees changes — the first decides whether the local network can still see where you went, the second decides how a site judges where you are.
To get the bigger picture of what a VPN solves in the first place, the article mentioned at the start covers that from the ground up — read together, "what it is" and "how it works" cover the whole thing. FastOrange handles exactly this path — one tap to connect, nodes chosen automatically — and every registered account gets free trial time each day. Signing up and connecting once says more than finishing this page does.
 High speed
 Millions of users
 24/7 Support
Get the Fast Orange App
One App. Every Platform. A More Stable Connection.
Available for Windows, macOS, Android, and iOS. Use One Account Across All Your Devices and Start with a Free Trial.
High speedMillions of users24/7 SupportDownload Fast Orange
 Choose your platform
Download Fast Orange
Switch between Windows, Android, iOS, and macOS